Defined by NIST to describe the non-linear stages of the incident handling process.
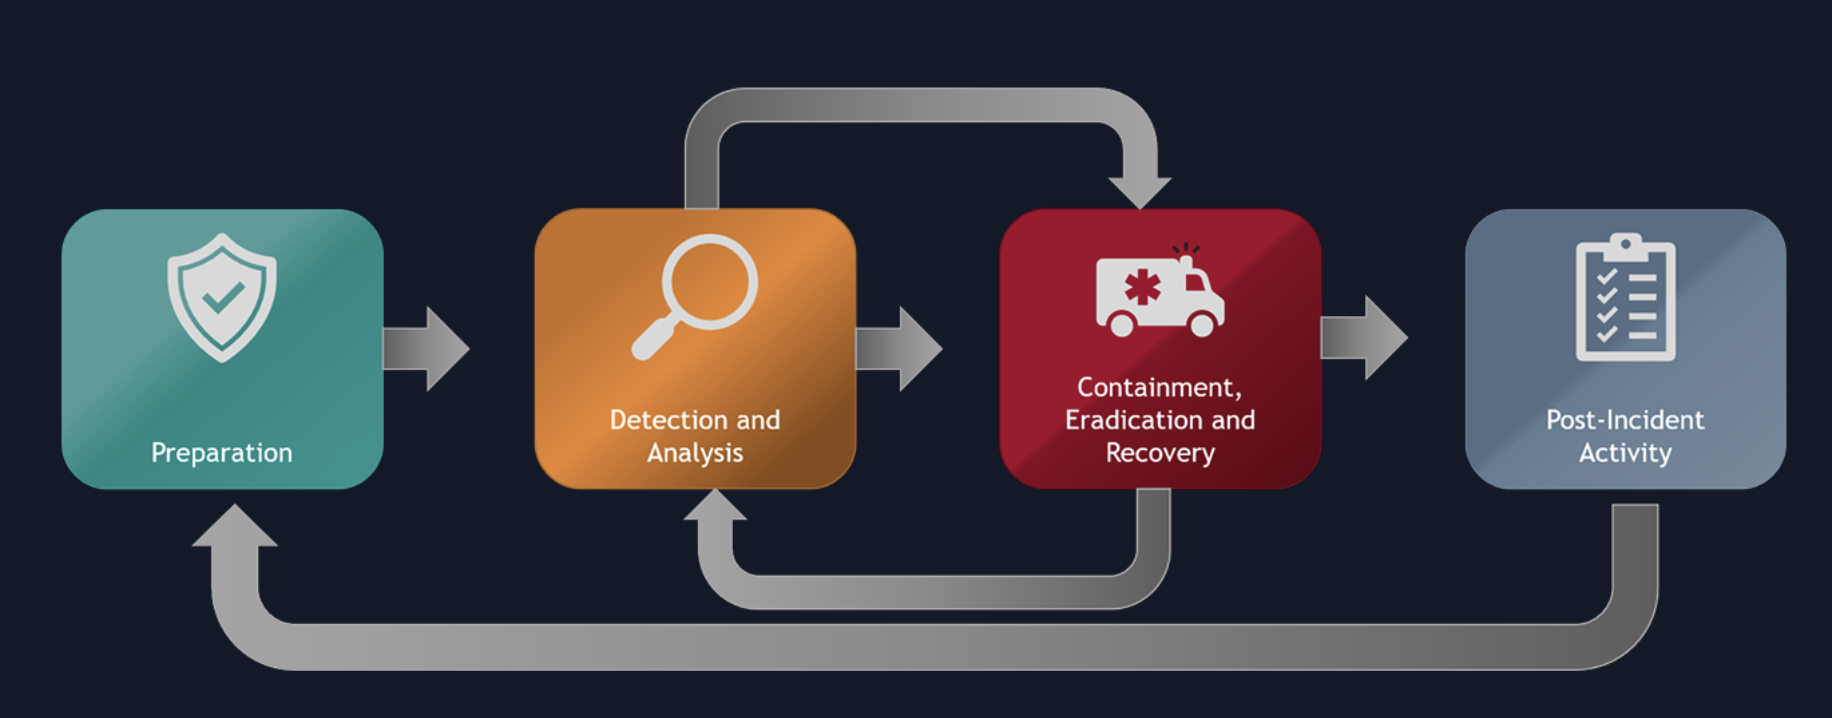
Preparation stage
During the preparation stage, we need to ensure that we have:
- Skilled incident handling team members (incident handling team members can be outsourced, but a basic understanding of incident handling are necessary in-house regardless).
- A trained workforce (through security awareness activities or other means of training).
- Clear policies and documentation.
- Tools (software and hardware).
Detection and Analysis
This stage starts when an incident has happened and we only have limited information about it. This limited information is used in a repeated 3-step process that iterate as the investigation evolves:
- Create and use IOCs.
- Identify new leads and impacted systems.
- Collect data and analysis from these new leads and impacted systems.
Containment, Eradication and Recovery
The previous stage provided understanding of the incident and its consequences, and now its time to prevent it from causing more damage.
Containment
The first part of this stage is to prevent the incident to spread.
Actions performed in this step is divided into:
- Short-term containment, e.g. pulling network cables or isolating systems on isolated VLAN.
- Long-term containment, e.g. change user passwords, apply firewall rules, system patch, or shutting down systems.
The containment actions should be coordinated and executed across all systems simultaneously, to prevent the attacker from learning of the containment tactic and adapt.
Eradication
When the incident is contained it should be completely eliminated from the systems and it should be ensured that all adversaries are out or the systems and network.
Recovery
Once the incident is eradicated recovery can start by bringing systems back to normal operation. It should be verified that these systems works as expected and that they contain all necessary data.
The systems should be subject to heavy logging and monitoring in some time after the incident to ensure that the adversaries does not regain access.
Post-Incident Activity
When the incident is past and systems are recovered this stage begins by documenting the incident to learn from it and prevent it in the future.
The result of this is an incident report.